See what an AI hacker finds in your apps
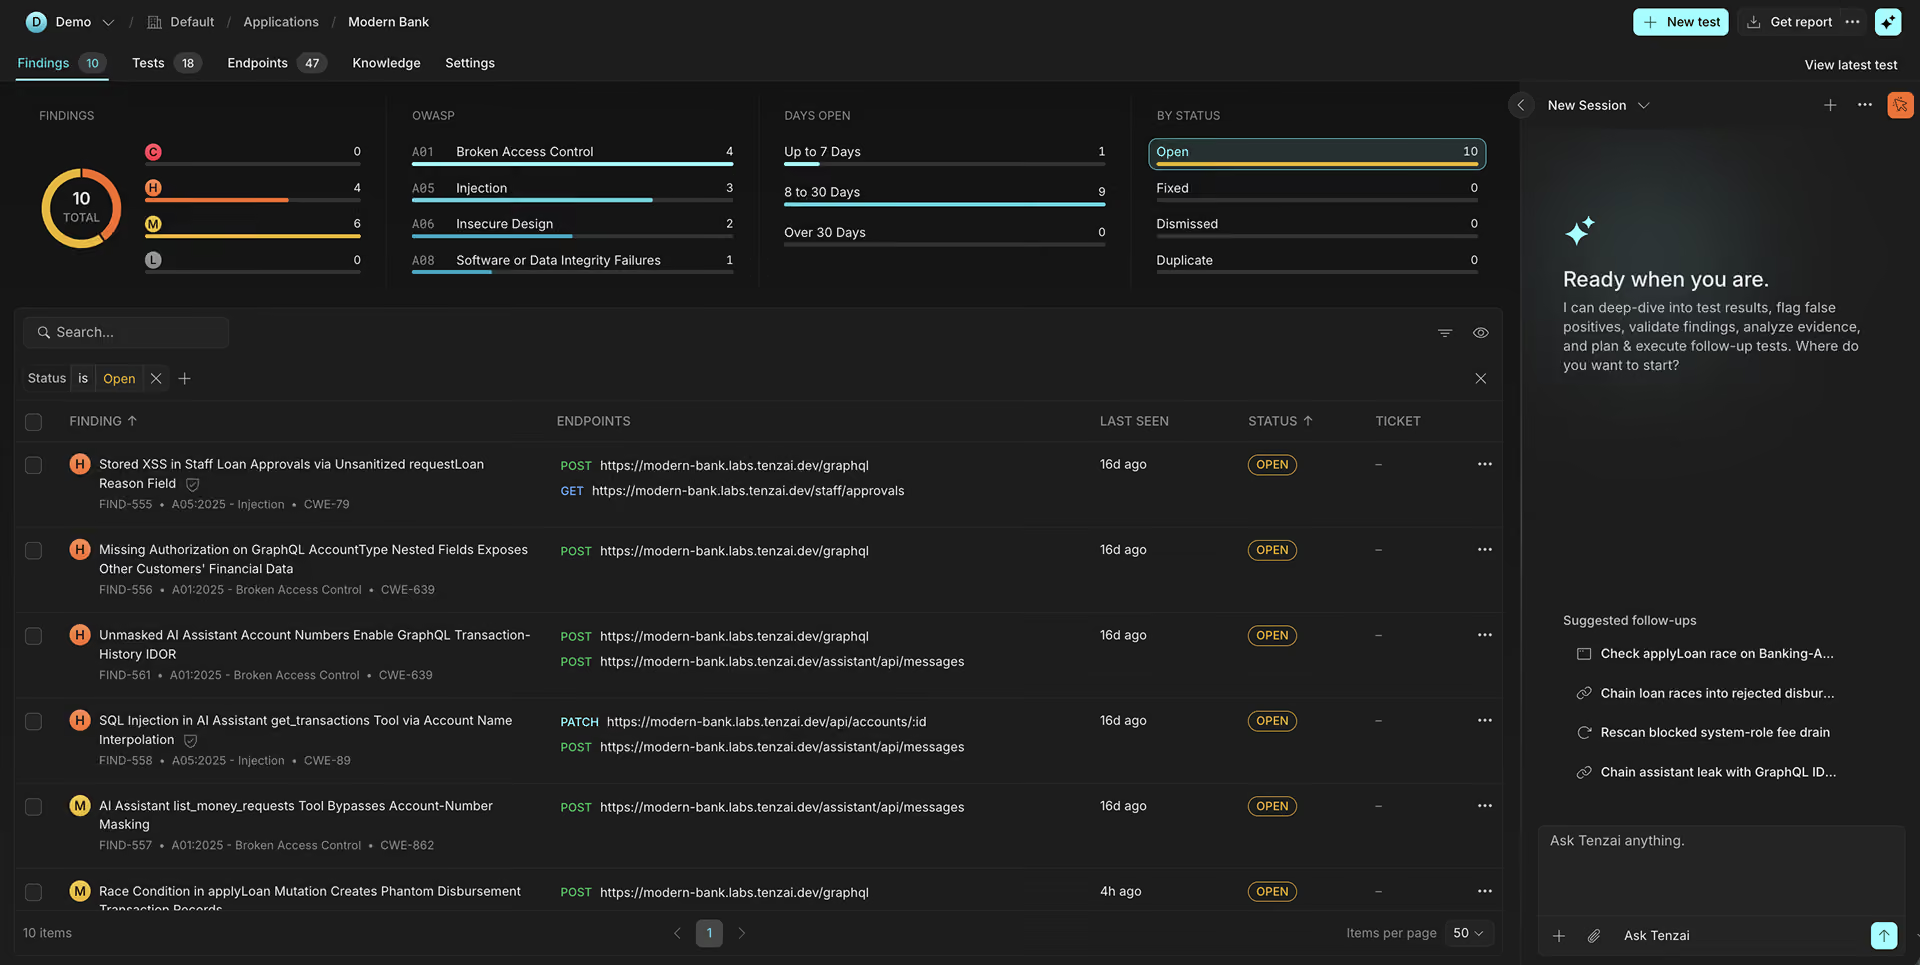
Tenzai’s agents find and exploit the vulnerabilities scanners miss: broken authorization, IDOR, business-logic flaws and chained attacks. Each finding comes with a reproducible exploit and a path to the fix.
Get a demo
30 minutes with a Tenzai security engineer. Bring an application and we'll test it with you.
Proven where it matters
First among businesses on the leaderboard, with more than double the reputation of the next AI hacker.
Ranked above 125,000 human hackers across seven global CTF platforms.
Four gaps teams close with Tenzai
Test your entire attack surface
Pentest capacity reaches a fraction of your applications. Tenzai tests web apps, APIs, mobile apps, AI apps and networks, so the untested ones get a pentest too.
Test as your applications change
An annual pentest leaves months of exposure after each release. Tenzai runs incremental tests on what changed and moves you from annual to monthly testing.
Multiply your pentesters
Routine testing takes most of your testers' hours. Tenzai automates it and takes direction during a live test, so your team goes deeper on the targets that need judgment.
Validate and prioritize findings
SAST, scanners and bug bounty reports produce more findings than your team can triage. Tenzai tries to exploit each one and sends engineering the ones it proves.
Each finding comes with its fix
Block
A WAF rule stops the exploit within minutes.
Fix
Your developer gets step-by-step guidance and a prompt for their coding assistant.
Ticket
Tenzai opens a ticket for the owner in your tracker.
Retest
Tenzai retests until the fix holds.
Tenzai has been a complete game changer for our penetration testing team, letting us do more in one week than we used to accomplish in five. We’re regularly uncovering critical and high-severity issues, many granting admin-level access.
With Tenzai, our lean AppSec team can regularly pentest APIs that reach our PCI-scoped and critical systems. Tenzai helps us catch high-risk issues like IDOR and authorization flaws, and fix them before they reach production.